How it works
From what you run to what to fix.
Ovesion checks published vulnerabilities against your exact versions, turns them into a short list of fixes, and explains every answer.
01 · Tell Ovesion what you run
Two ways, used together.
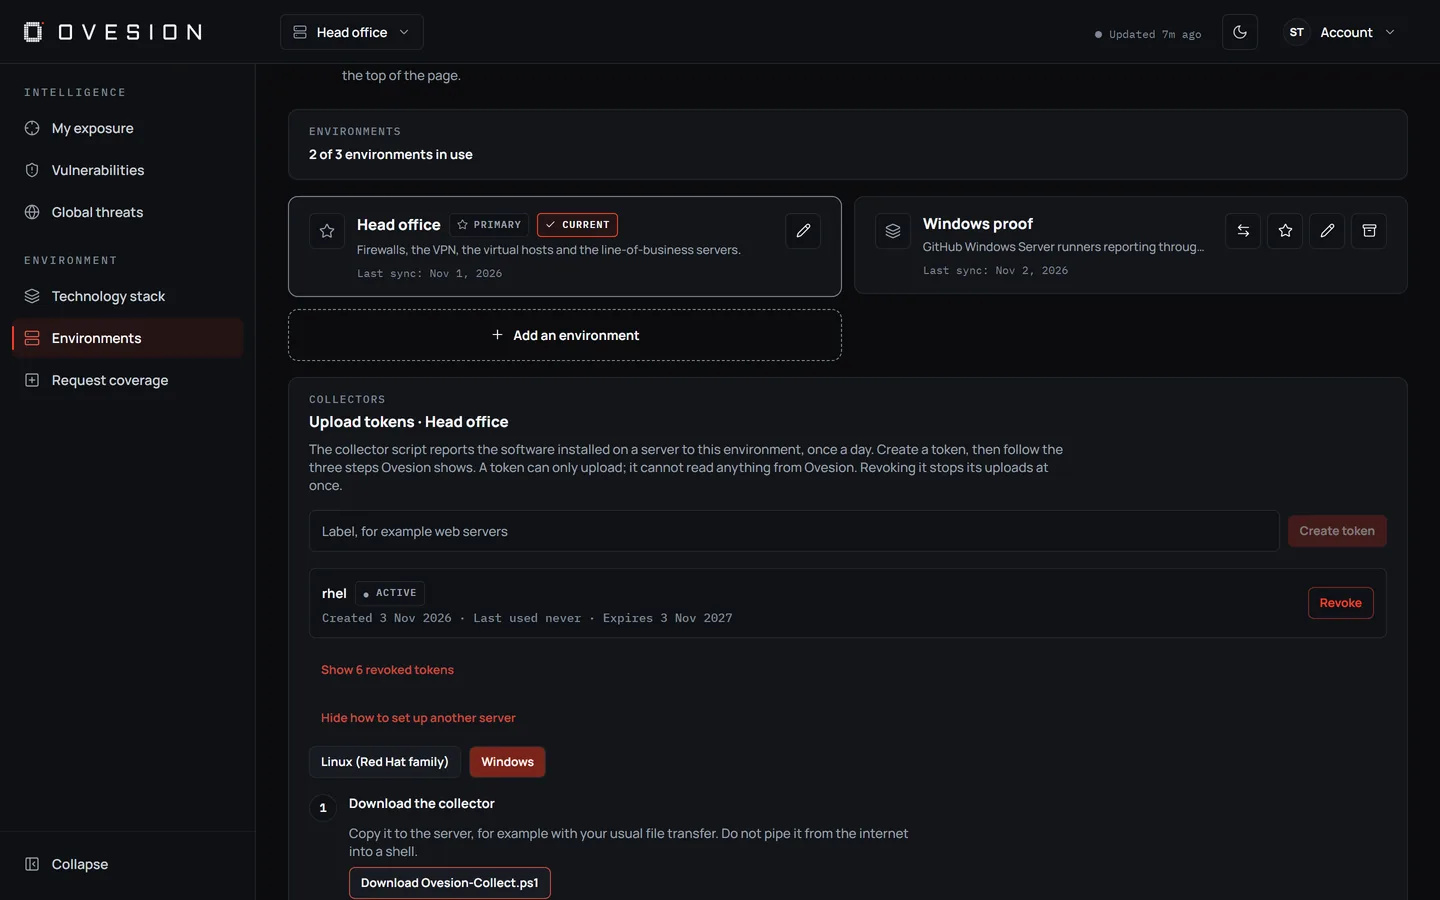
Run a collector
A short script reports the software on your Linux and Windows servers once a day. See supported systems
Type in what has no collector
Firewalls, appliances and applications, by product and version.
02 · The fix plan
Follow one fix to its decision.
- 01
One row per fix.
Ovesion groups CVEs by the fix that closes them. Each row says what to do, how many CVEs it closes and how many are being exploited.
- 02
See why it ranks here.
The drawer names the deciding CVE, the remediation steps and which source said what.
- 03
The inputs, in plain words.
Act, Exploited now, Likely next, Automatable, Reach and Job size. Each card is one input to the decision.
- 04
One public decision.
The CERT/CC SSVC method turns those inputs into one of four decisions. This fix is Immediate.
Built from the demo account’s real fix plan
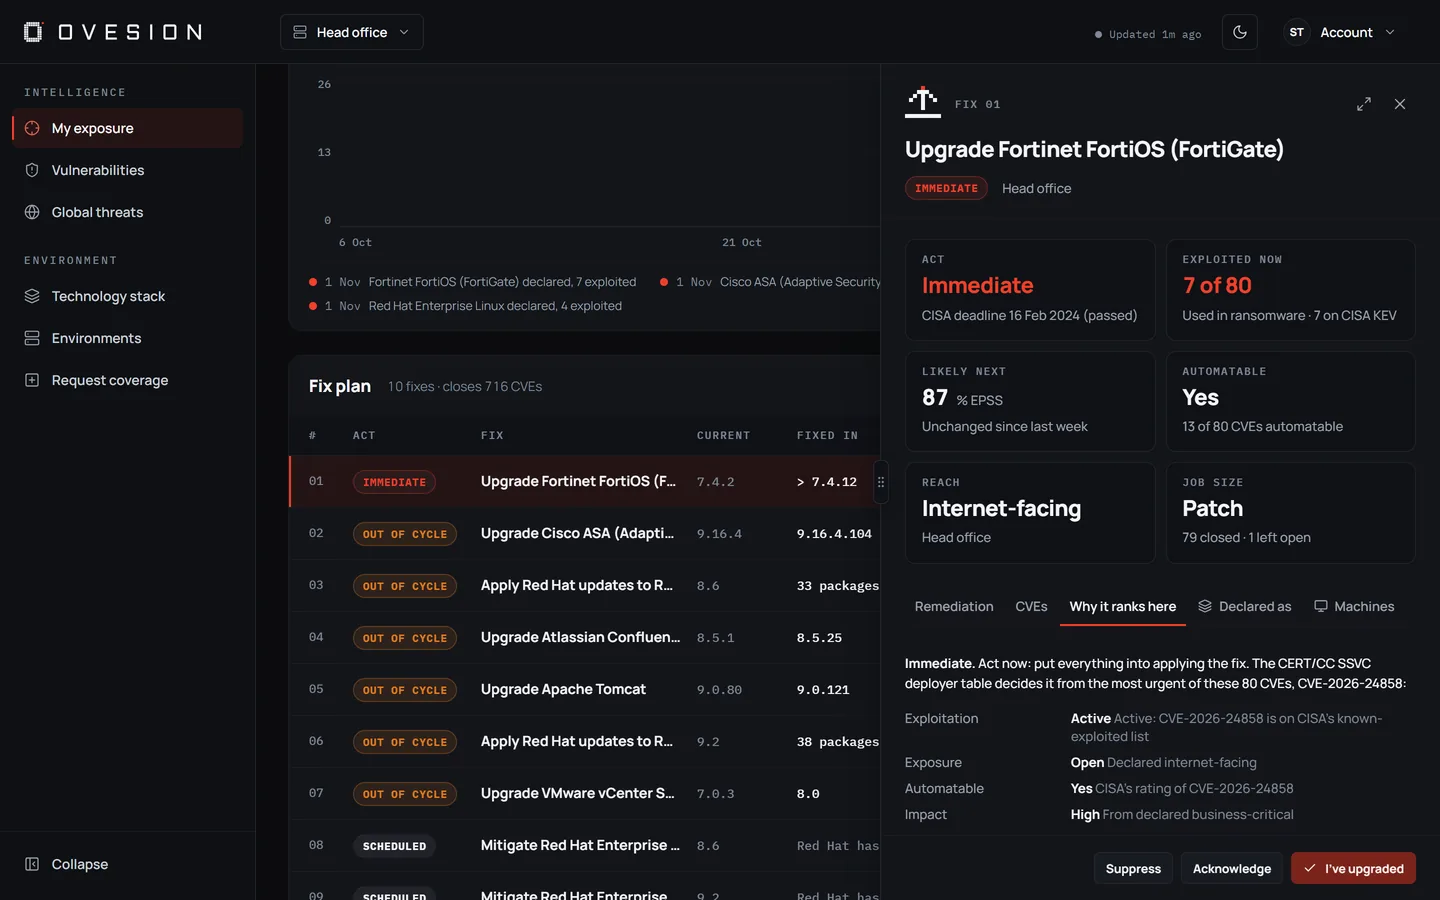
Why it ranks here.
The deciding CVE and which source said what, for every fix.
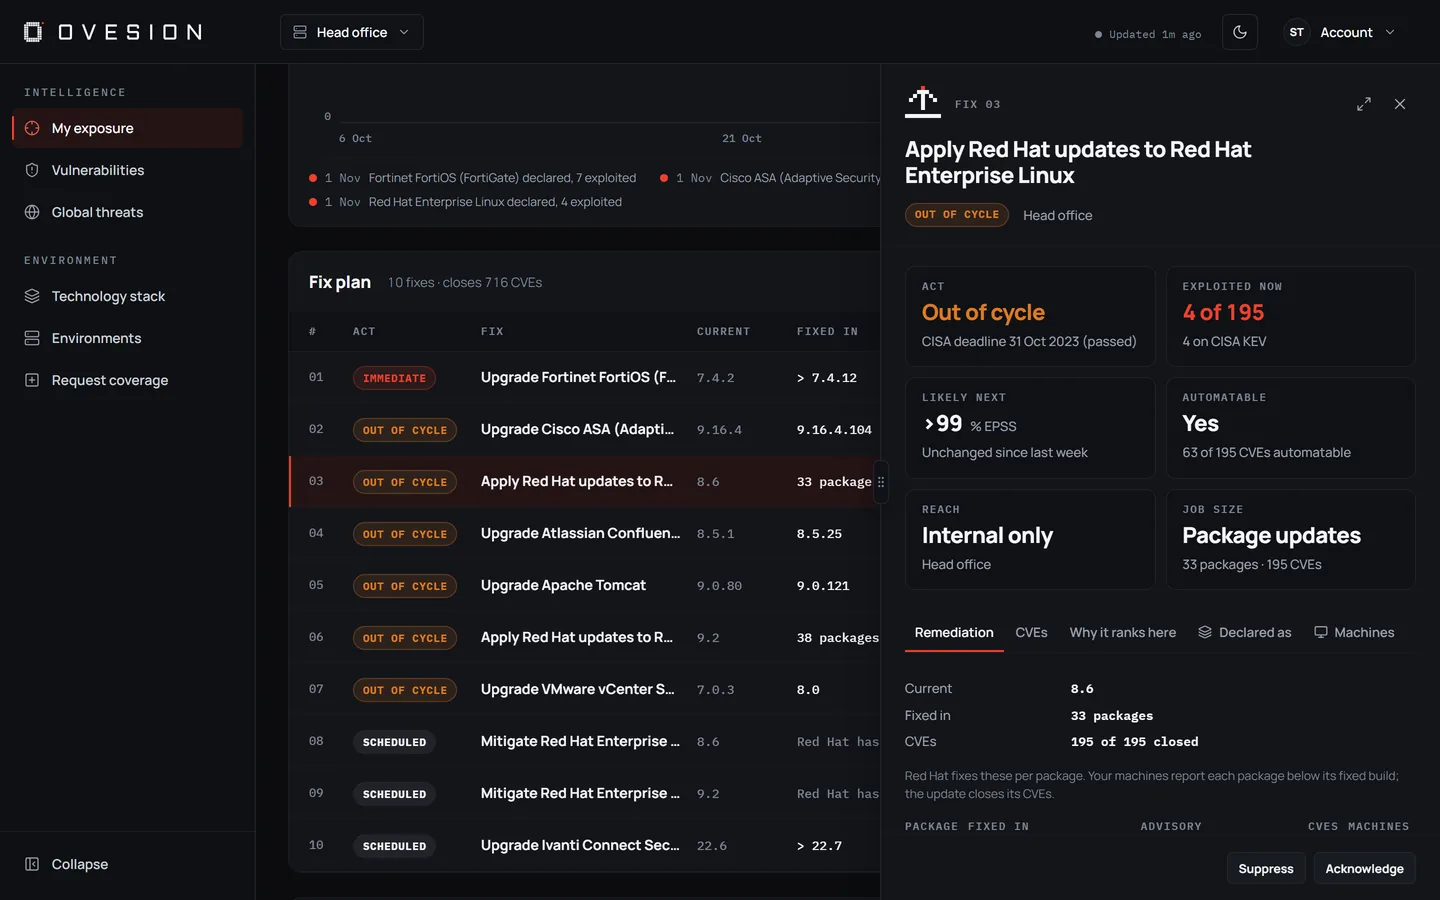
The exact package updates.
For machines reporting through the collector, a Red Hat fix lists the package updates that close it, from Red Hat’s own data.
03 · Urgency
Four decisions, in plain words.
Each fix gets a public, explainable decision from the CERT/CC SSVC method. There’s no opaque 0 to 100 score. Try it on the home page
Act now: put everything into applying the fix.
Act before your next maintenance window, at the next opportunity.
Apply in your regular maintenance window.
No action yet. Ovesion keeps watching it.
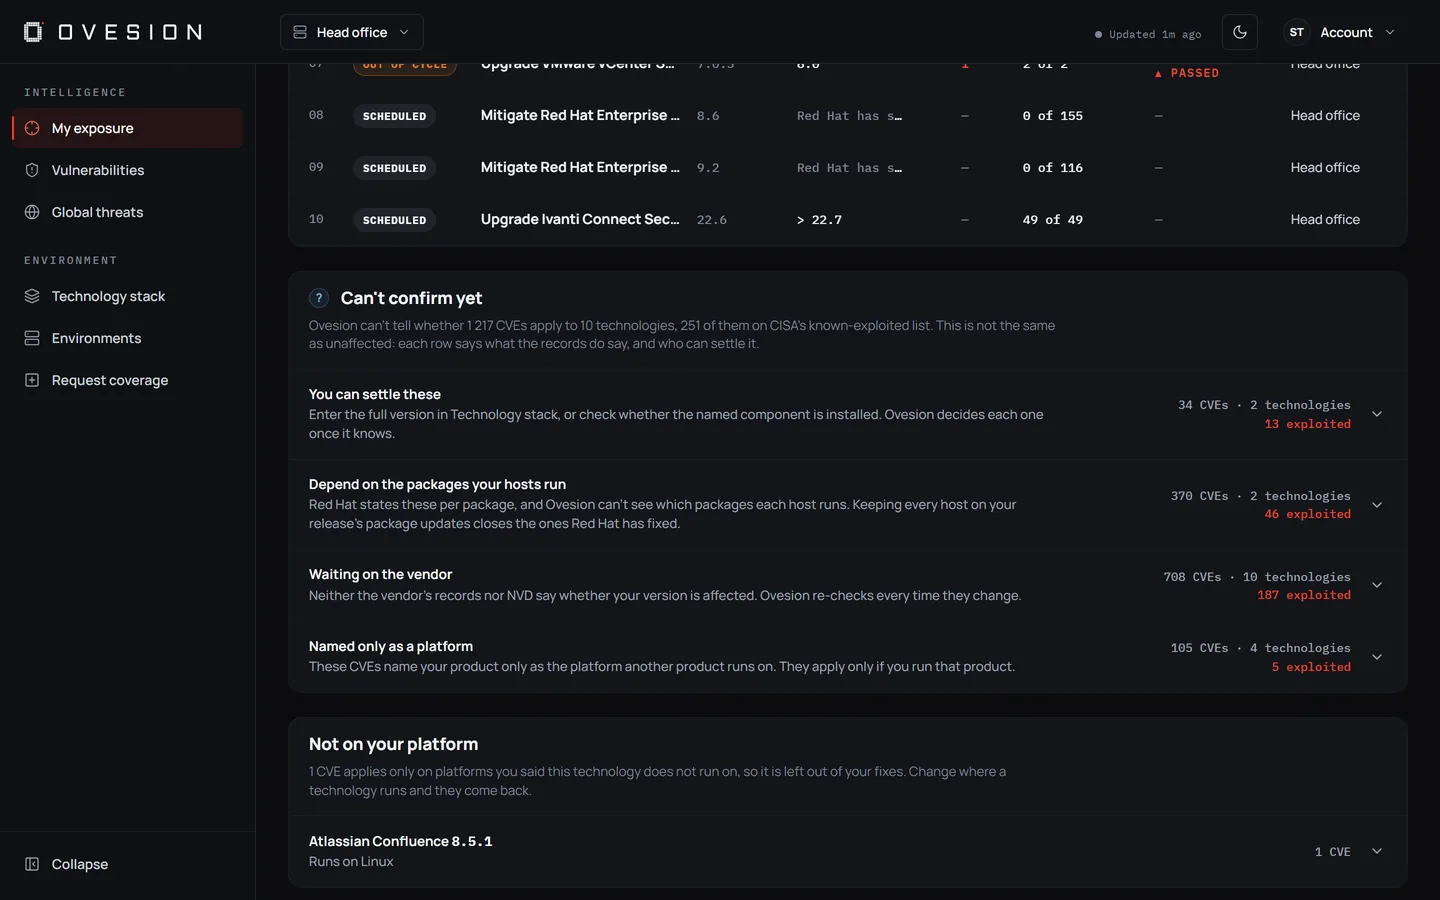
Can’t confirm
Honest about what it can’t decide.
Can’t confirm lists what the records don’t settle, and who can settle it: you, the vendor or Ovesion. Ovesion never says “safe”.
Stay informed
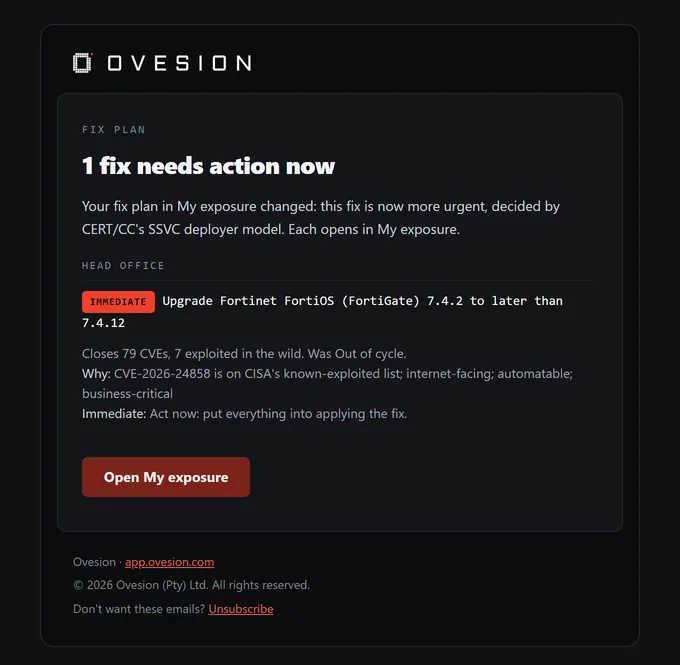
An alert when a fix becomes urgent.
An email when a fix becomes urgent, with the reason, and a correction if an answer changes. Unsubscribe in one click.

Ovesion
Ovesion: 1 fix needs action now
04 · Also in Ovesion
Look wider, work as a team.
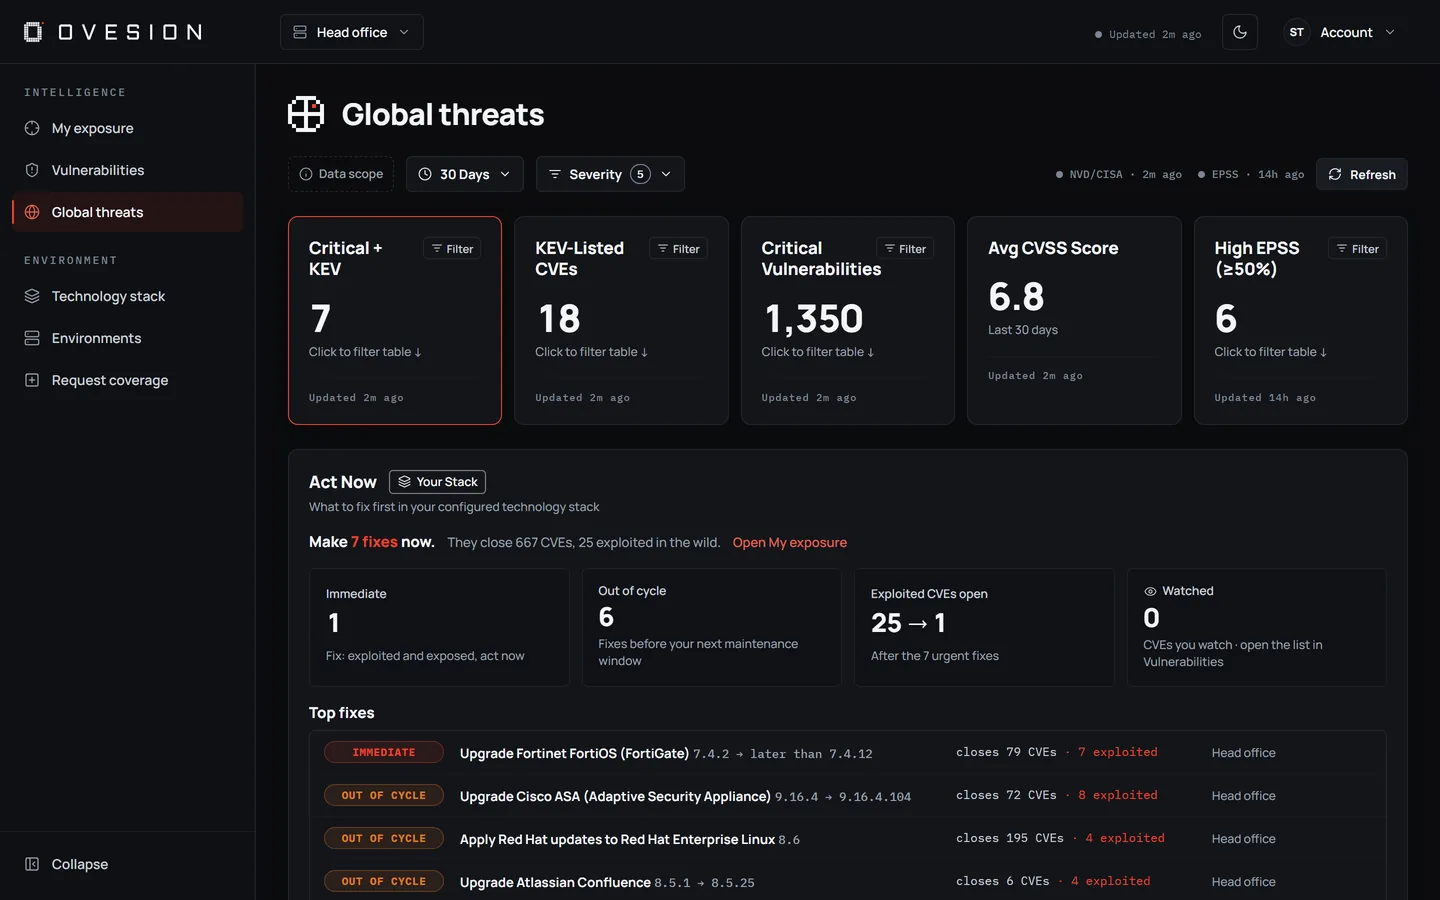
Global threats and CVE search
What is new and exploited worldwide, with a personal watch list, free for everyone. On paid plans, a searchable CVE list with CSV export.
Roles
- Owner
- Everything, including billing and admins.
- Admin
- Manages the team, the environments and their stacks, and reviews findings.
- Vulnerability analyst
- Reviews findings and keeps the technology stacks up to date.
- Viewer
- Sees the environments and their findings.
Each person holds one environment or all of them.
Roles for your team
Admin, vulnerability analyst or viewer, for one environment or all of them. An account can require an authenticator app for everyone.
See your own fix plan.
No agent. A readable script you run yourself.